Does your MFA provider support offline Windows Logon and RDP authentication?
April 18, 2022 •
Last reviewed: September 2026
Are you a Windows user and need remote access to your laptop or desktop? With remote work continuing to permeate our workplaces, logging in remotely to a Windows system persists as a common and often insecure activity that users across the globe perform every day.
Many administrators correctly want to add a layer of security to that login process with multi-factor authentication (MFA), but have concerns about implementation, usability, and limiting users’ login options.
There are fair concerns, but it’s important to remember that not all MFA providers are made equally!
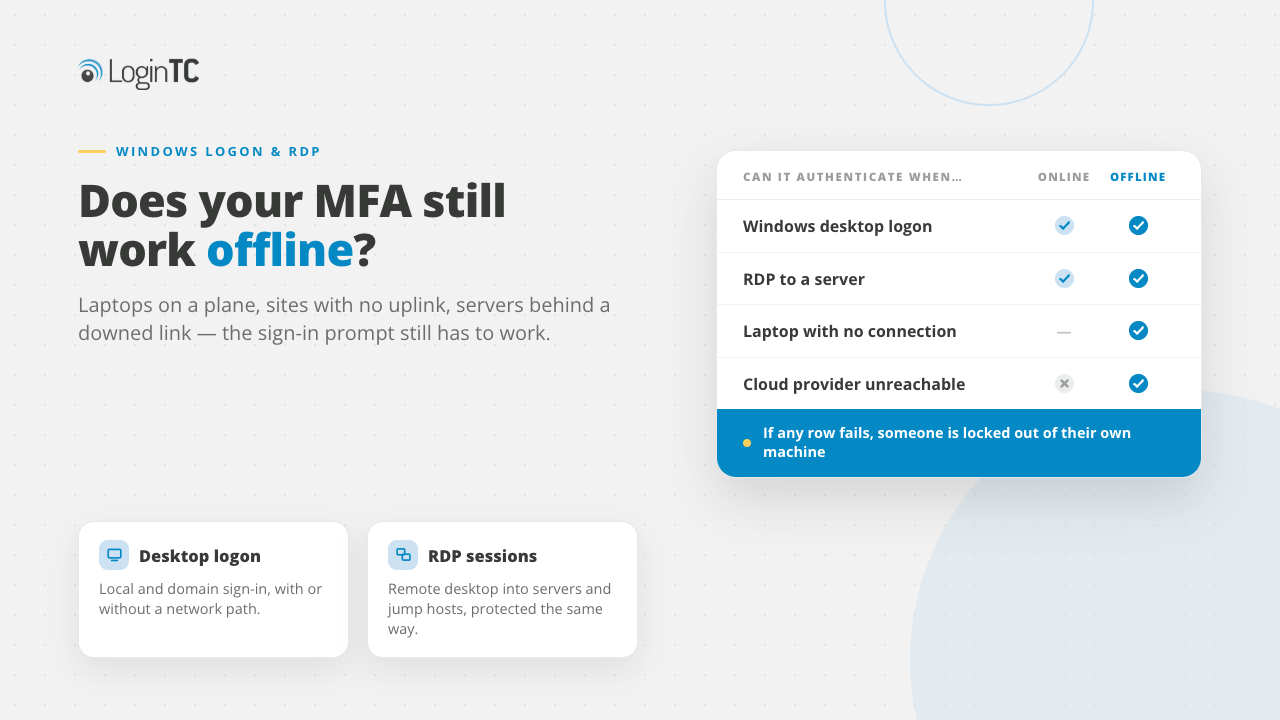
Securing remote access to Windows with LoginTC MFA makes it easy for end users to enroll and log into Windows Logon and RDP protected applications, and easy for administrators to manage. Part of the reason why LoginTC is the preferred solution for many users and administrators is that it works both online and offline for Windows Logon. This unique technology allows users to stay secure no matter where they are and what connection they have.
How exactly is LoginTC able to do this? Let’s dive deeper.

As we know, LoginTC acts as the authenticator for your MFA protection on your device. With Windows Logon you have multiple options that work both online and offline for Windows logon. When signing in to your account: online authentication methods such as Push notifications, Software OTP (generated in LoginTC app), Hardware token, SMS, Phone call, and Bypass codes. There are also offline authentication options: QR scan, passcode grid, security key, hardware token, authenticator app and offline bypass code. Six methods, covering users with a phone, users with a token, users with a printed card and users with nothing but a call to the help desk.
But exactly what problem does the Windows Logon Connector solve?
Normally, Windows allows users to log in when offline and the only time it wouldn’t is if the computer’s administrator configured it that way. Even if it’s configured that way, adding a second factor of authentication is difficult because it wouldn’t be invoked until after the user enters their correct username and password.
The problem that the LoginTC QR scanner solves is let’s say an administrator is security conscious (not a bad thing!) and restricts their users laptops to require a network connection to their corporate network; the LoginTC Windows Logon & RDP Connector could potentially relax that requirement knowing that LoginTC would add offline MFA. Windows allows users to log in when offline using the QR Code scanner.
The QR scanner works like this: Once you enter your username and password, the LoginTC window will then be invoked, showing a QR code for you to scan. Once you scan the QR code in the app, it will display a 6-digit code, allowing you to login securely, all while being completely offline. The great thing about this feature is that you can still utilize first factor password authentication while also leveraging your two-factor authentication process.
Another option for offline authentication are Offline Bypass codes. To login offline using this method, the user must enter a 9-digit Offline Bypass Code, which can be given to them by their IT administrator. Offline bypass codes are generated each time a user logs in online and can be found on the users page in the LoginTC Admin Panel. You can read more about offline bypass authentication here.
The six offline methods, and who each one is for
An offline method is only useful if your user is actually carrying what it needs. That is why the list is six long rather than one.
- Security key. Insert the key and press it. A FIDO2 signature is checked against a registered public key rather than a shared secret, and that check can be performed on the machine, which is why it survives a loss of connectivity. For users who already carry a key for other systems, this is the strongest option available offline.
- Hardware token. The same one-time-passcode token already assigned to the user works offline.
- Authenticator app. The same software token already assigned to the user works offline.
- QR scan. The user scans a code on the sign-in screen with the LoginTC mobile app and enters the six-digit response. Supported on the LoginTC iOS and Android apps.
- Passcode grid. The user enters the three-letter tuples corresponding to their own passcode grid. For users with no phone and no token at all.
- Offline bypass code. A nine-digit code issued by the help desk, for the genuine emergency. The number of issued codes can be capped by policy, and codes regenerate each time the user signs in online.
There is no separate enrolment step for any of this. As the connector documentation puts it, “offline methods are only available if the user has logged in online at least once.” One successful online sign-in registers the user automatically, with the methods already assigned to them.
The question behind the question: does it fail open?
This is what to actually ask a vendor, because it is the difference between a control and a suggestion. When the MFA service is unreachable, does the product let the user through on their password alone, or does it require a second factor from a locally verifiable method?
A product that fails open has a documented bypass: an attacker who can interfere with the machine’s network path can remove your second factor. LoginTC does not fail open. When the service cannot be reached, the user is required to complete an offline method. The corollary is worth planning for: that guarantee depends on you enabling the offline methods your users actually carry, because a fleet with offline authentication switched off will fail closed and lock people out.
Limits you should set deliberately
Offline access is not meant to be unbounded, and the policies guide gives you the controls to bound it. The three worth deciding on before you roll out are Offline Days Limit, which caps how many days a machine can keep authenticating away from the network, Successful Offline Login Limit, which caps it by count instead, and Invalid Offline Login Limit, which caps offline brute-force attempts. One operational note: policy changes take effect the next time the user signs in online, so a machine that has been offline for a fortnight is still running the policy it last collected.
For the mechanism behind offline security key sign-in specifically, see FIDO2 Windows login, online and offline. For the step-by-step on each method, see how to use offline MFA for Windows logon and RDP.
Frequently asked questions about offline MFA for Windows logon
Which offline authentication methods does LoginTC support for Windows logon?
Six: QR scan, passcode grid, security key, hardware token, authenticator app and offline bypass code. Which of these a given user sees depends on the methods assigned to them and the offline methods enabled in your policy.
Do users have to enrol separately for offline authentication?
No. Offline methods become available once the user has signed in online at least once, which registers them automatically with the methods already assigned to them. Plan for that one online sign-in when you image a machine or hand over a laptop.
What happens if an MFA provider cannot reach its own service during a Windows login?
That depends entirely on the product, and it is the most important question to ask during an evaluation. Some products fail open, meaning the user is admitted on their password alone when the service is unreachable, which gives an attacker a bypass they can trigger by interfering with the network. LoginTC requires the user to complete an offline method instead.
Can a user authenticate offline with no phone and no hardware token?
Yes. A passcode grid is a printed card of three-letter tuples that requires no device at all. If the user does not have one either, the help desk can issue a nine-digit offline bypass code.
How long can a machine keep authenticating offline?
As long as you allow. Offline Days Limit caps it by days and Successful Offline Login Limit caps it by number of sign-ins, both set per organisation, application or group in your policy. Neither is a setting you should leave at its default without a decision.
If you want to learn more about offline authentication and all the authentication methods that LoginTC offers, reach out at sales@cyphercor.com.