FIDO2 Authentication with Windows Logon and RDP is here
November 29, 2023 •
Last reviewed: September 2026
This post announced FIDO2 support in connector version 1.4.0. For current behaviour, including why the FIDO2 ceremony still completes when a machine is offline and what the built-in Windows options cannot do on on-premises Active Directory, see FIDO2 Windows login, online and offline.
LoginTC’s latest product update brings phishing-resistant FIDO2 authentication to the Windows Logon and RDP Connector. This innovative use of security key authentication is game-changing for administrators who want complete peace of mind over their multi-factor authentication (MFA) operations.
Keep reading to learn what this update means for FIDO2 authentication at LoginTC.
What is FIDO2 Authentication?
FIDO2 tokens are specifically designed to safeguard against phishing attacks. The tokens utilize robust encryption algorithms to shield the user’s credentials. As a result, it becomes extremely challenging for attackers to intercept or modify the user’s credentials.
FIDO2 tokens are also simple to use for end-users. FIDO2 tokens work by inserting the key into a USB port in their computer and tapping a button. This method is fast and works without an external connection to additional services.
The WebAuthn protocols underlying how the FIDO2 tokens operate are also standardized for compliance, meaning you can use this authentication method to comply with a variety of regulations, insurance requirements, and government legislation.
What is unique about LoginTC’s FIDO2 for Windows solution?
FIDO2 keys leverage information in your browser to confirm the correct credential is used to authenticate into a user’s account. Because of this, most use cases for FIDO2 tokens are web-based applications and pages.
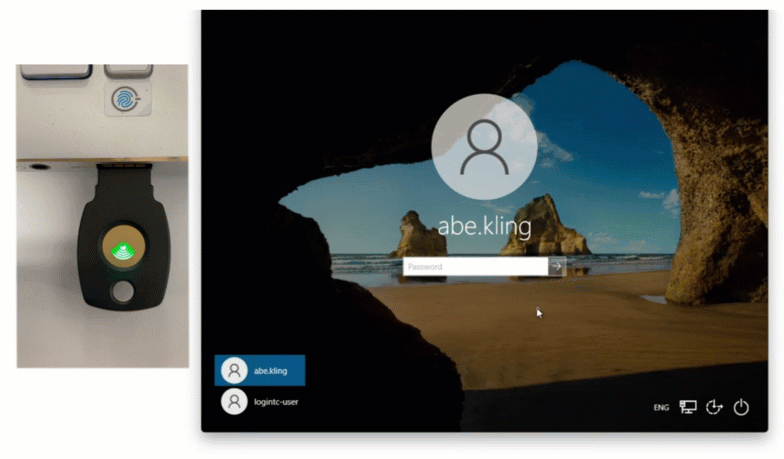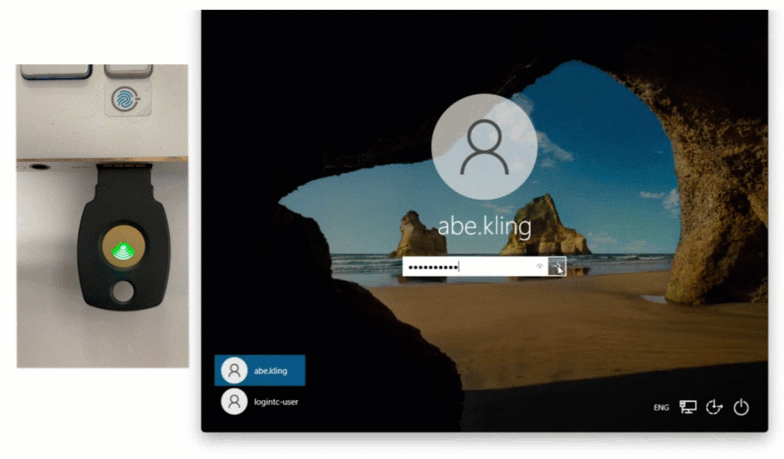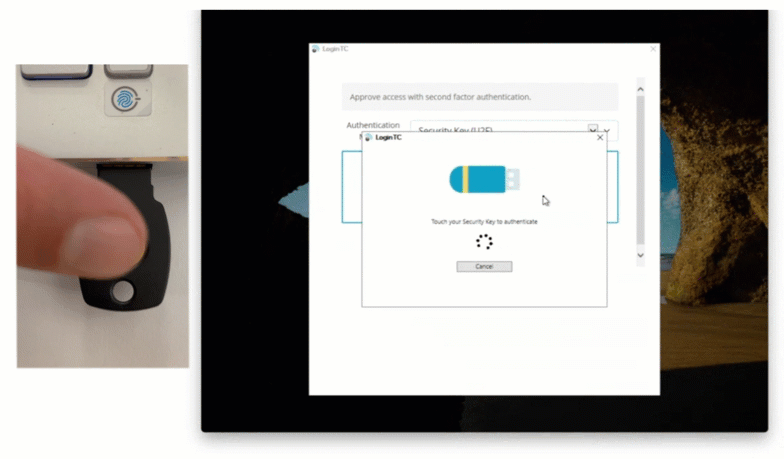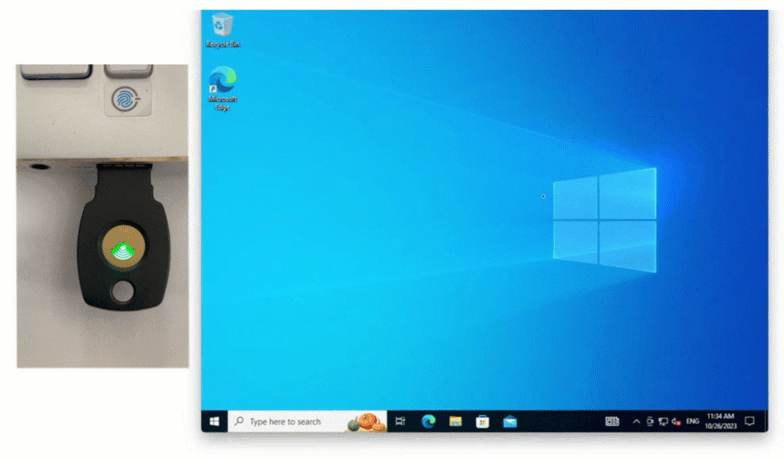
LoginTC has developed a way to leverage FIDO2 keys to authenticate access to Windows logins — a service that doesn’t traditionally interact with the browser. This utilization of FIDO2 opens the door to phishing-resistant authentication available anywhere.
Read on to learn how to use FIDO2 with LoginTC.
How does FIDO2 work with the LoginTC Windows Logon and RDP Connector?
FIDO2 authentication can be used in a number of ways with LoginTC. Explore each of those use cases below:
Remotely
You can use your FIDO2 authentication token to login with Remote Desktop. Using services like RD Web and RD Gateway, you can securely authenticate to a remote machine with a FIDO2 token by inserting it into the machine being used to establish the Remote Desktop connection.
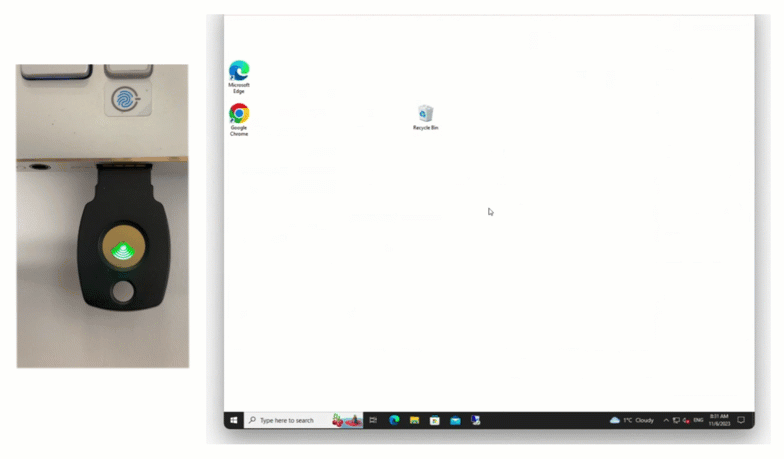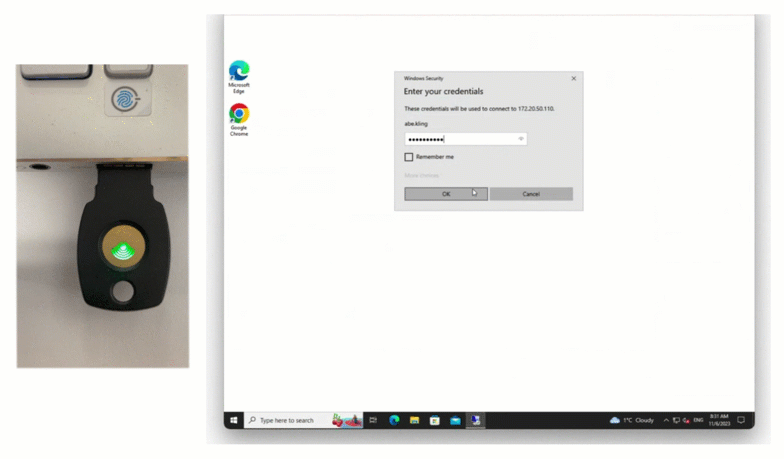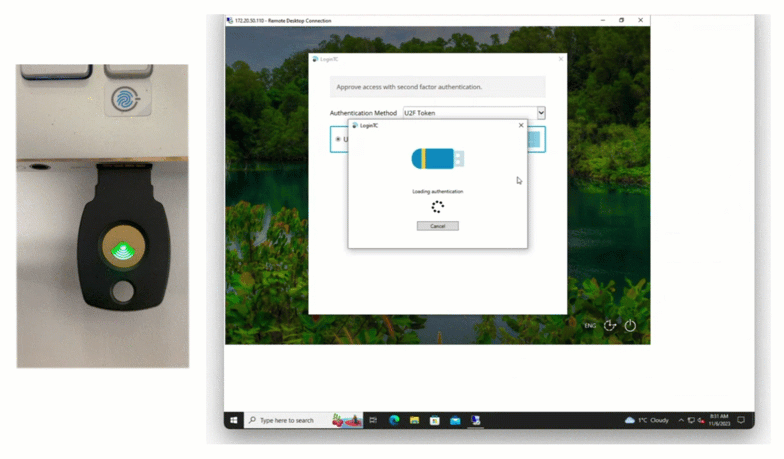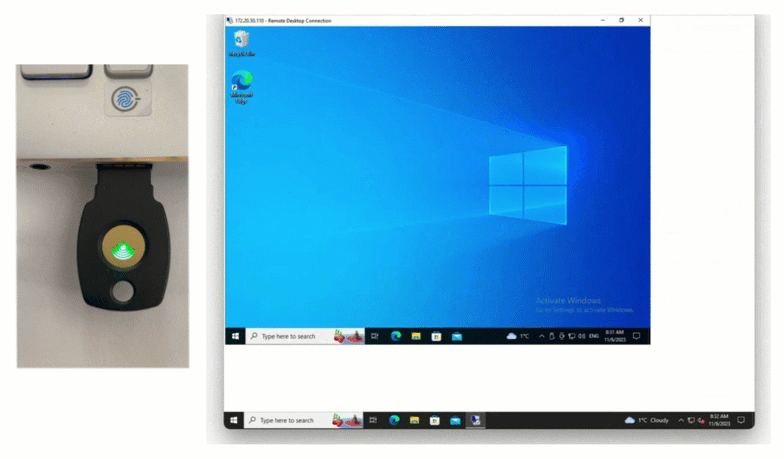
This functionality means you can bring FIDO2 authentication anywhere you go.
Online
You can use FIDO2 keys to authenticate to Windows online. LoginTC’s unique configuration allows for a seamless and fast authentication experience when logging into Windows and RDP.
Offline
FIDO2 authentication can also be used for offline authentication to the Windows Logon and RDP connector.
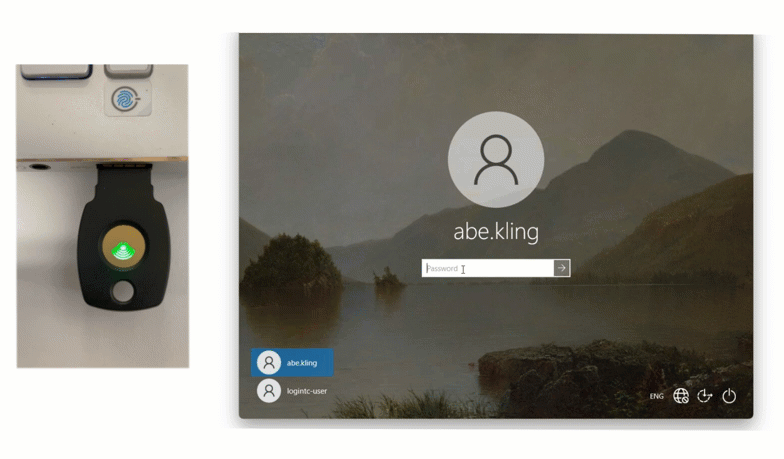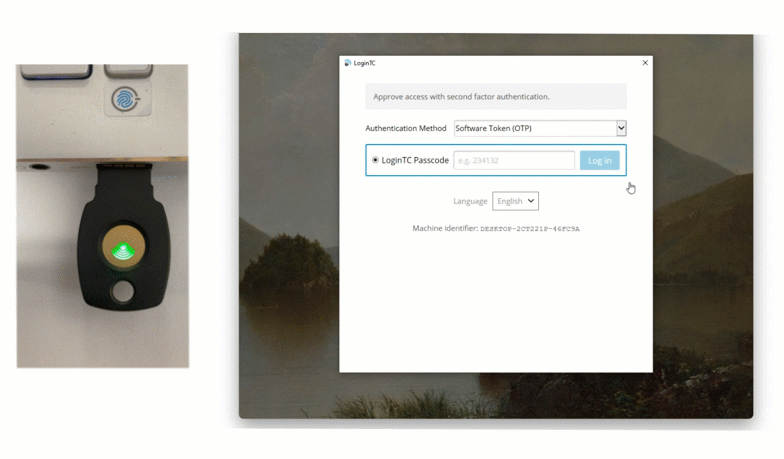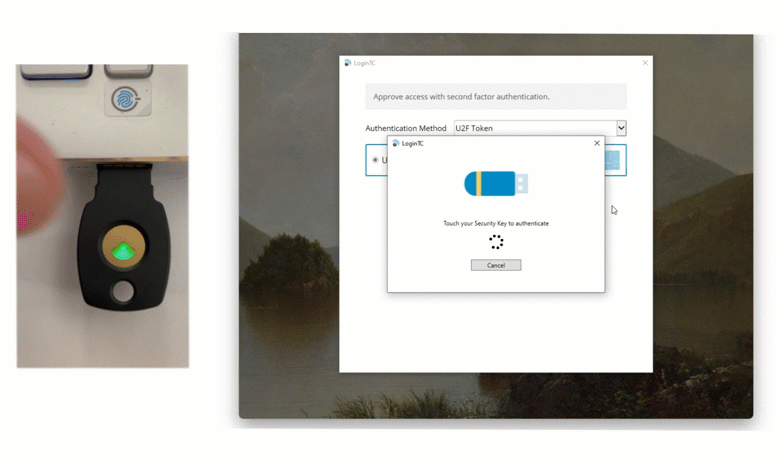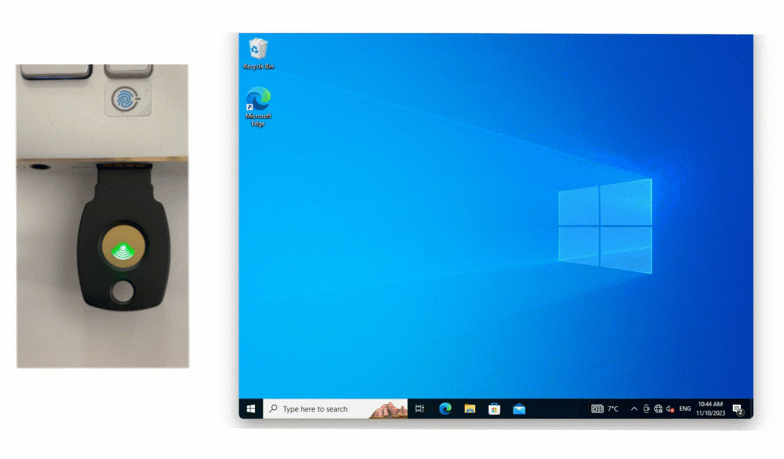
Even if your users are logging into a computer that isn’t connected to the internet, secure FIDO2 keys can be used for second factor authentication.
Cloud
Authenticate with FIDO2 tokens in the cloud version of our LoginTC Windows Logon and RDP connector. Leverage the simplicity of LoginTC Cloud with the security of phishing-resistant FIDO2 authentication.
Read more about FIDO2 and LoginTC here
On-Premises
FIDO2 authentication can also be used with our on-premises MFA solution, LoginTC Managed. Administrators don’t have to choose between added control over their security operations, or the most secure authentication method available.
Get it all with FIDO2 authentication in the Windows Logon and RDP Connector for LoginTC Managed.
Read more about it in our latest update to LoginTC Managed
Start using FIDO2 for the Windows Logon and RDP Connector
Existing customers get FIDO2 by upgrading to the current version of the Windows Logon and RDP Connector. FIDO2 support arrived in version 1.4.0 in November 2023, and the current release line is 2.0.0. Check the connector release notes for the latest build and the download page for the installer that matches your machine architecture.
If you’re looking for secure, phishing-resistant authentication for your organization, start a LoginTC free trial today.
Frequently asked questions about FIDO2 for Windows Logon and RDP
Which connector version added FIDO2 support for Windows logon?
Version 1.4.0 of the LoginTC Windows Logon and RDP Connector, released in November 2023. Later versions built on it: 1.4.5 added FIDO2 smart card support in August 2025, and 1.4.7 added biometric FIDO2 chip card support in April 2026. The current release line is 2.0.0. The full history is in the connector release notes.
Which LoginTC plan includes security keys for Windows logon?
Security keys, offline authentication and the Windows Logon and RDP connector are all included on the Cloud Business and On-Premises Managed plans. See pricing for the current tiers.
Do I need a cloud identity to use a security key at the Windows sign-in screen?
Not with the LoginTC connector. It is a native Windows credential provider that adds the security key as a second factor against your existing on-premises Active Directory, without changes to your directory structure. This is worth knowing because Microsoft’s own native FIDO2 Windows sign-in does not support on-premises-only Active Directory Domain Services deployments and requires Microsoft Entra joined or Entra hybrid joined devices.
Which Windows versions does the connector support?
Windows Server 2016, 2019, 2022 and 2025, and Windows 10 version 1607 or later and Windows 11, on x64 or ARM64, with a native ARM64 installer as of version 2.0.0. Windows Server 2012 R2 and Windows 8.1 are supported by connector version 1.4.x and earlier only.
Is this the same thing as passwordless Windows login?
No. The user enters their Active Directory username and password and then satisfies the second factor with the security key. That is phishing-resistant multi-factor authentication rather than passwordless sign-in. See what is phishing-resistant MFA for where the line sits.