Posts by Lisa Trumbley
-
FIDO2 for Windows: How Security Key Login Works Online and Offline
September 18, 2026 •
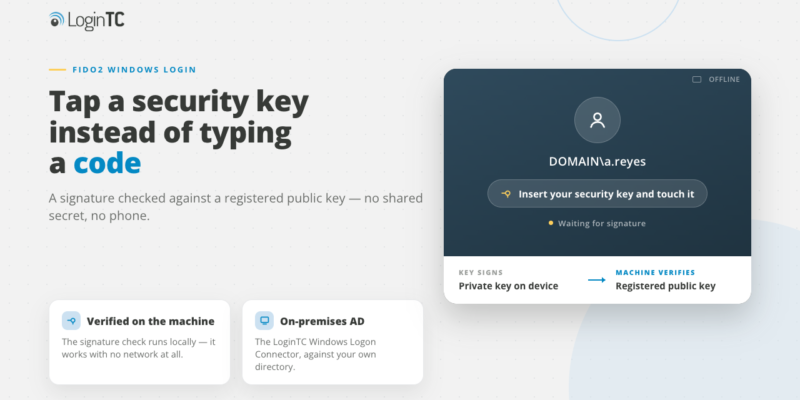
FIDO2 Windows login means presenting a hardware security key at the Windows sign-in screen instead of typing a code from a phone. What the key produces is a signature checked against a registered public key, not a shared secret, and that check can be performed by the machine itself. With the LoginTC Windows Logon Connector […]
-
September 09, 2026 •
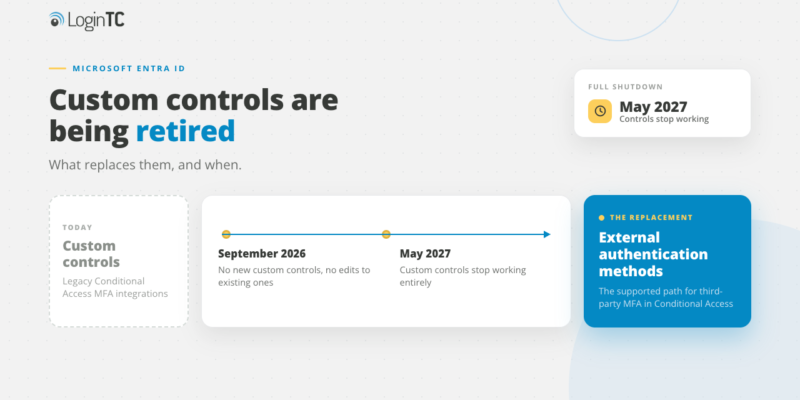
Microsoft is retiring Conditional Access custom controls, the mechanism most organizations used to connect a third-party MFA provider to Microsoft Entra ID before external authentication methods existed. From September 2026 you can no longer create a custom control or edit an existing one. In May 2027 custom controls stop working entirely. The replacement is external […]
-
The Identity Pillar of Zero Trust: Where Your MFA Sits and What Moves You Up
September 02, 2026 •
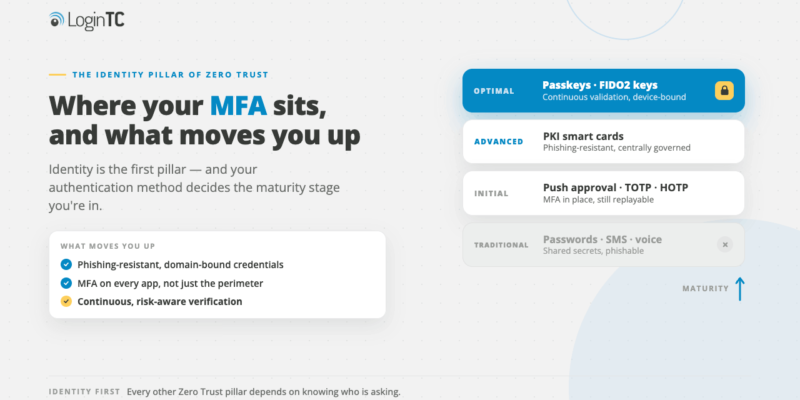
Identity is one of the five pillars in the CISA Zero Trust Maturity Model, and each pillar is assessed across four stages: Traditional, Initial, Advanced and Optimal. For authentication, the practical difference between stages is not how many factors you use but what kind. Passwords with basic MFA sit at Traditional. Phishing-resistant methods such as […]
-
August 28, 2026 •
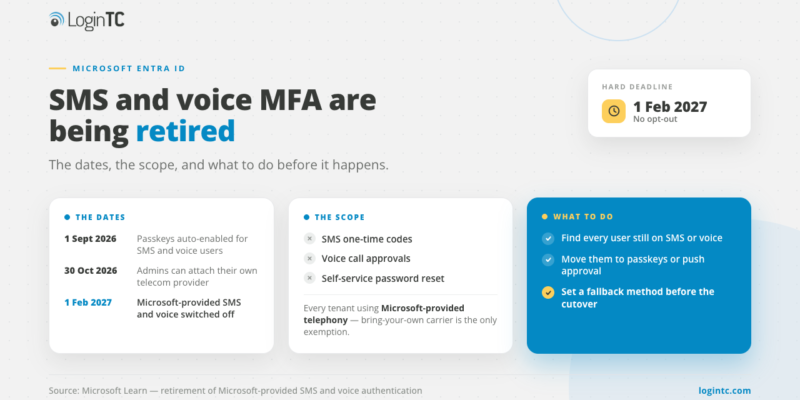
Microsoft is retiring the SMS and voice delivery it provides for multi-factor authentication in Microsoft Entra ID on 1 February 2027. Before that, on 1 September 2026, passkeys become the default authentication experience and users currently enabled for SMS or voice are automatically enabled for passkeys and prompted to register. If you still need SMS […]
-
What is Phishing-Resistant MFA? A Plain-Language Guide
August 09, 2026 •

Quick answer: Phishing-resistant MFA is a category of multi-factor authentication that uses cryptographic binding between your device and a specific website or server. Because the credential is mathematically tied to the legitimate domain, attackers cannot intercept or replay it on a fake site. FIDO2/passkeys and certificate-based authentication (CBA) are the two methods that currently qualify. […]
-
Passkey Active Directory Integration: 2026 Guide for IT Admins
July 10, 2026 •
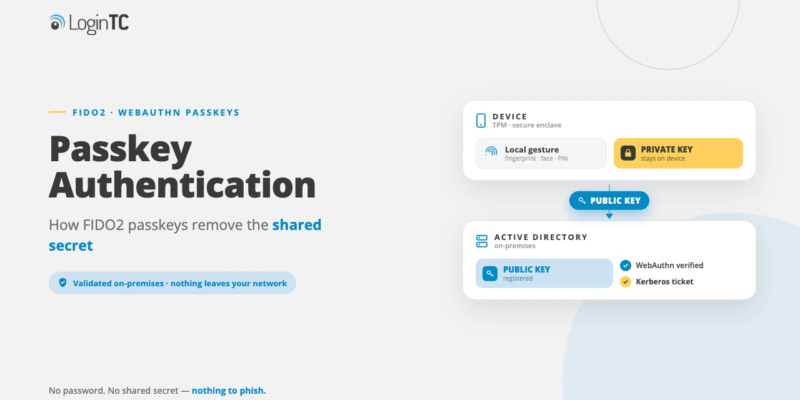
Passkeys can integrate with Active Directory through two primary paths. The first is hybrid Azure AD, using Microsoft Entra ID’s FIDO2 security key support. The second is on-premises deployment, using third-party identity bridges or RADIUS-based MFA solutions. Neither path requires a full cloud migration. Your existing AD infrastructure can support passkey authentication today with the […]
-
UK School Phone Ban: What IT Admins Must Know About MFA
June 18, 2026 •
The United Kingdom’s forthcoming statutory phone ban in schools is sending ripples far beyond the classroom. For school IT administrators, the disruption is not just about confiscating handsets at the gate. It strikes at the heart of how staff and students currently authenticate into school networks, applications, and managed devices. If your institution relies on […]
-
MFA Integration with Active Directory: The Non-Invasive Approach
May 11, 2026 •
If you manage a Windows environment, Active Directory (AD) is almost certainly the backbone of your identity infrastructure. It controls who accesses what, enforces Group Policy, and authenticates users across your entire organization. But here is the uncomfortable truth: Active Directory was not designed with modern threat actors in mind. Stolen credentials remain the leading […]